In business, risk management identifies, assesses, controls, mitigates, and monitors potential risks (negative and positive) to manage their consequences for an organisation.
This article focuses on risk identification.
Key Takeaways
- Definition & Importance: Risk identification is the foundational process of uncovering, recognising, and describing potential threats that could impact a business’s operations, finances, or reputation
- When to Act: Risk identification should begin at the start-up phase of a business and be treated as a continuous process rather than a one-off event
- The 3 Best Starting Methods: For businesses establishing a risk strategy, combining Brainstorming (team-driven insights), SWOT Analysis (internal strengths/weaknesses), and PESTEL Analysis (external macro-environmental factors) offers the most comprehensive initial coverage
- 19 Diverse Frameworks: Effective risk discovery requires a mix of qualitative, quantitative, and collaborative tools, ranging from data-driven approaches like Root Cause Analysis and FMEA to creative exercises like Affinity Diagrams and Scenario Analysis
- The Ultimate Goal: The objective is not just to list problems, but to document them clearly in a Risk Register so they can be prioritised, mitigated, and monitored to protect business continuity.
What is the risk management process?
There are five steps to any effective risk management process:
- Risk Identification (this article)
- Risk Analysis
- Risk Assessment and Risk Evaluation
- Risk Control and Risk Mitigation
- Risk Monitoring
What is risk identification?
A risk identification process identifies and documents potential negative and positive risks that could prevent or enable an organisation to reach its objectives. To do this, you must ask questions about every aspect of the business, such as: what could go wrong?
There are many ways to identify risks.
The most important thing is to be systematic and rigorous in the approach and use the right tools and techniques. Ask the right questions to identify the correct possible risk sources. Once complete, enter all risks into a risk register.
Why is risk identification important?
Risk identification enables organisations to develop plans to manage positive or negative risk events before they arise.
The objective is to identify all risk events that could harm business operations, such as lawsuits, theft, technology breaches, and business downturns, and positive risks that, if managed correctly, could help an organisation achieve or exceed business goals.
When should risk identification be undertaken?
Risk identification should begin early in business operations, i.e., during the start-up phase, when uncertainty and risk exposure are highest and risk management can have the greatest impact.
Identifying risks early also allows risk owners to act when risks are usually simpler to manage.
Risk owners who execute early responses often reduce costs compared to addressing a significant risk and issue later in the project or business lifecycle.
What are the risk identification methods?
Risk Identification methods are established tools for analysing business operations (internal and external) and discovering threats and opportunities.
The most popular techniques in risk management are shown in the next section.
19 methods to identify risks
These are provided in alphabetical order:
Affinity Diagram
An affinity diagram organises information into categories based on their similarities.
Participants propose potential company risks and file each response under a few categories. For example, they can be financial, schedule, or safety risks. This separates risks into categories for expert review and helps organise the feedback. From there, the participants can assess, prioritise and address each risk.
Assumption Analysis
Assumptions Analysis explores the accuracy of business assumptions and identifies risks to the business around inaccuracy, inconsistency, or incompleteness.
Bow Tie Analysis
Bow Tie Analysis identifies where new or enhanced controls may be worthwhile. It is a core part of risk management, particularly where risk is high or control effectiveness is assessed as low.
Brainstorming
Brainstorming brings together stakeholders in the business.
It allows participants to speculate ideas, share facts, consider the future business, and identify risk events.
Brainstorming is one way to identify risks; the risk events listed may come from those on the front lines of the business who are more familiar with day-to-day operations.
You can run a brainstorming session regularly to determine what stakeholders see as the business’s most significant risks.
Business Plans
A business plan is a basic outline of the organisation and its needs. This includes material and labour needs, the business timeline, and any associated risks.
A detailed business plan can help you understand the organisation’s culture and what it takes to reach its goals.
It also informs stakeholders about what they’re investing in, tracks team progress, and offers a return on the initial investment.
Cause and Effect, Ishikawa, or Fish-bone diagrams
These diagrams help you search for root causes, identify problems, and compare the importance of different causes.
Exploring the causes and continually asking why or how for each cause leads to better risk analysis and understanding of the problem.
Checklists
A risk checklist is the final risk-identification step to ensure common risks are not overlooked.
What is it?
Risk checklists are historical lists of lessons learned, previously identified risks, or risks realised in the past. They are meant to be shared among all stakeholders.

Delphi
The Delphi method takes its name from a religious sanctuary dedicated to the Greek god Apollo. Developed in the eighth century B.C., the sanctuary was known for divining the future and was consulted before all major undertakings.
The Delphi technique involves sending questionnaires to experts and stakeholders and compiling their responses without linking opinions to the people who suggested them.
The responses are then returned to the same group for further qualitative risk analysis or amendments.
Stakeholders and experts provide risk opinions anonymously, without influencing one another.
Direct Observations (dynamic risk assessment)
Although not a specific risk-identification technique, direct observation plays a prominent role. Establishing a culture of lifelong risk awareness is the best way for businesses to be prepared for any risk.
Assigned personnel are the first to sense threats or opportunities and take the necessary measures.
Direct observations can also be known as dynamic risk identification.
Failure Mode and Effects Analysis (FMEA)
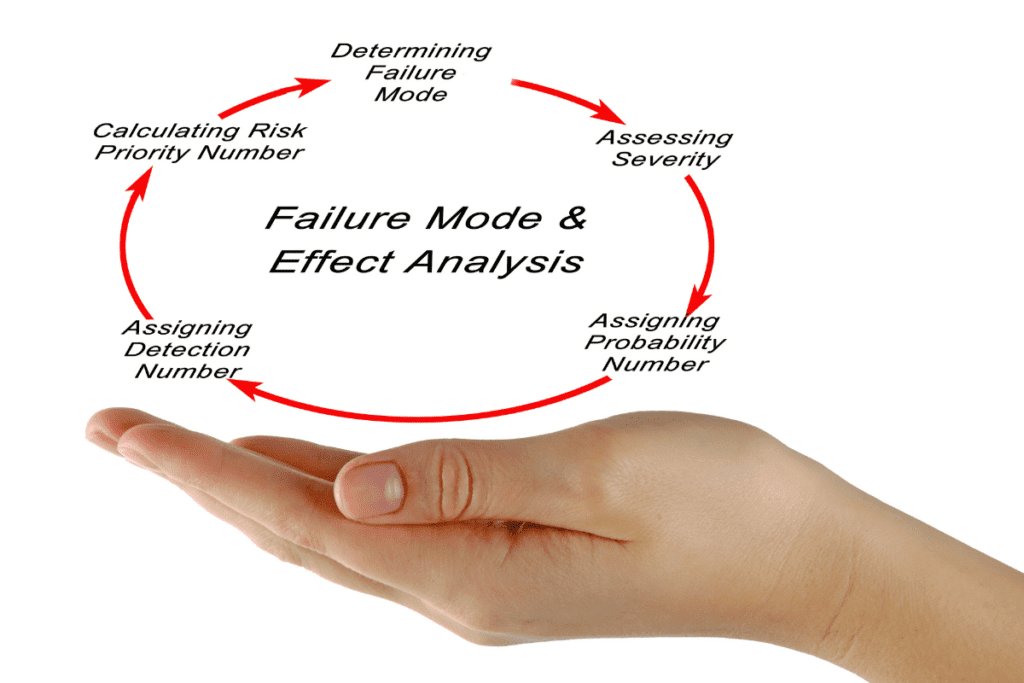
Failure Mode and Effects Analysis identifies failures that pose the greatest overall risk to a process, product, or service.
This risk identification technique identifies the following:
- Failure mode: How a product can fail, or deficiencies or defects
- Effect of failure: The consequences of a particular mode of failure
- Cause of failure: The causes of an observed mode of failure
- Analysis of the failure mode: Its frequency, severity, and chance of detection
Fault Tree Analysis (FTA)
Fault tree analysis (FTA) is a visual method to explore the causes of system-level failures.
It uses Boolean logic to combine lower-level events. It is a top-down approach to identifying the component-level failures (basic events) that cause the system-level failure (top event).
Fault Tree Analysis consists of two elements:
- Events
- Logic gates: connecting the Events to identify the cause of the undesired event
Incident Analysis
Incident analysis methods are used in many different sectors and cover a range of specific techniques, including:
- Root Cause Analysis
- 5-Whys
- Incident Bow-tie
- Systematic Cause Analysis Technique (SCAT) Analysis
Interviews With Stakeholders
Stakeholders are people with an interest in the business.
Interviewing them helps better understand what they believe are the most significant risks.
Stakeholders often invest significant resources in a business. They may provide an external perspective on risk and help the company understand stakeholders’ concerns and how to address them.
Nominal Group Technique (NGT)
The NGT, or Nominal Group Technique, is a brainstorming method that offers a more detailed approach to the subject matter.
The participants write their ideas about the risks without discussing them with other members. Then, the team leader asks for and collates each participant’s views, removing overlapping risks.
NGT depends on honesty and teamwork and provides a more comprehensive approach than Brainstorming. Participants discuss each item to ensure everyone understands it, then prioritise them.
PESTLE Analysis
PESTLE analysis is a process that identifies the Political, Economic, Socio-Cultural, Technological, Legal and Environmental risks in organisations.
PESTLE analysis may help assess risks arising from external factors. This may include tax policy, employment laws, environmental regulations, trade restrictions, tariffs, reform and political stability.
PESTLE analysis can be used with many other forms of risk identification, for example, within SWOT analysis.
Requirements Review
Requirements Review studies a business’s labour, material or financial needs.
It allows the participants to analyse requirements often and identify potential risks quickly.
The participants can complete a requirements review throughout the business timeline to understand risks and needs at each stage of the business lifecycle. During operation, requirements can change, which may also change the risk involved. For example, suppose a process requires twice as much material as initially speculated. In that case, the business’s financial risk rises because of additional costs.
Root Cause Analysis
A root cause analysis investigates previous business risks and how they relate to one another and the current project. The root cause can be a financial risk, old equipment, poor-quality materials, etc.
Finding the root cause helps the analysis identify common business challenges and minimise them for greater efficiency.
Scenario Analysis
In scenario analysis, you create different scenarios.
Scenarios are alternative ways to achieve an objective or analyse interactions in a market sector, for example.
Any event that triggers a desired or undesired scenario alternative is identified as a risk.
Structured “What-if” Technique (SWIFT)
Structured What-If Technique (SWIFT) is a hazard analysis method that uses structured Brainstorming with guidewords and prompts to identify risks faster than more intensive methods like Failure Mode and Effects Analysis (FMEA).
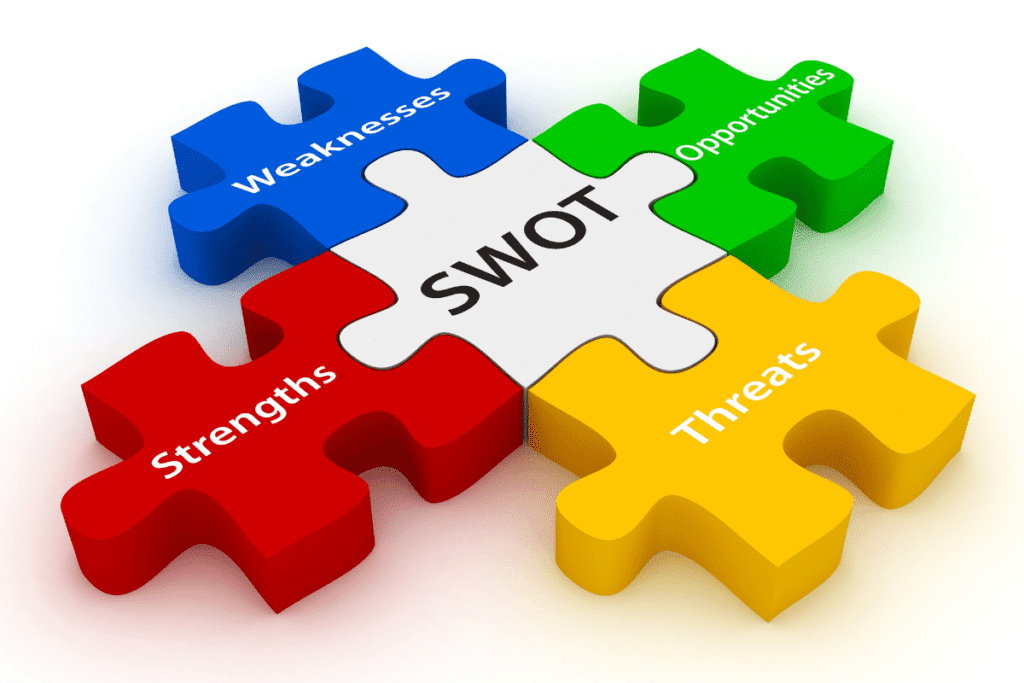
SWOT Analysis
Strengths, Weaknesses, Opportunities and Threats (SWOT) analysis is a way to understand a business’s risks alongside other important factors.
A SWOT analysis can show why a business or project is worth investing in and helps the business better understand its ability to reach goals.
A SWOT analysis examines four factors:
- Strengths: where the business excels
- Weaknesses: where the business can improve
- Opportunities: where the business can improve, grow or expand
- Threats: risks for the company and how it can minimise those risks
Risk identification errors
Many people make common mistakes in risk identification when managing business risks. These include:
- Risks are not captured in one place
- Not identifying risks correctly
- Only using a single risk identification method
- The failure to recognise risks early to allow management of the risk
- Risks are not identified with appropriate stakeholders
- The failure to make all risks transparent and available to all stakeholders
- Not aligning risk identification with organisational goals
- A project, departments, other divisions, etc., creating their risk identification framework
- Risk identification analysis and practitioners are disconnected from the business
- Not considering opportunities
- Not making risk identification an ongoing process
What risk identification methods should I use?
Businesses can use many risk identification methods to protect themselves.
The best method depends on the specific business and its risks.
The responsible risk manager should evaluate the business and provide the most suitable methods.
If you are inexperienced in risk management and want an overview, GetRiskManager suggests using Brainstorming with a SWOT analysis. The SWOT is supported within each section by a PESTLE analysis.
Once complete, the risks are reviewed for further identification through a different method.
Conclusion
Businesses can use many risk identification methods to protect and grow, but choosing the most suitable method is essential.
Frequently Asked Questions
What is risk identification?
Risk identification is the process of proactively finding, recognising, and describing potential threats and opportunities that could impact a business’s objectives, operations, or financial health.
Why is identifying risks important for a business?
Identifying risks allows a business to anticipate problems before they occur, allocate resources to protect assets, ensure regulatory compliance, and build a resilient strategy that can withstand market or operational disruptions.
When should a business perform risk identification?
Risk identification should ideally begin during the start-up or planning phase of a business and continue as an ongoing, regular process. Major organisational shifts, new project launches, or changes in industry regulations should also trigger it.
What are the best risk identification methods for beginners?
The most effective starting point for a business is a combination of Brainstorming (for collaborative team insights), SWOT Analysis (to map internal strengths and weaknesses), and PESTEL Analysis (to evaluate external macro-environmental factors like political and technological shifts).
How many risk identification methods exist?
While dozens of frameworks exist depending on the industry, 19 core qualitative and quantitative methods are widely recognised in risk management, ranging from creative exercises like Affinity Diagrams to highly structured models like Failure Mode and Effects Analysis (FMEA).
What happens after a business identifies its risks?
Once risks are identified, the business compiles them into a centralised document called a Risk Register. From there, the business analyses the likelihood and impact of each threat, prioritises them, and assigns specific owners to implement mitigation strategies.